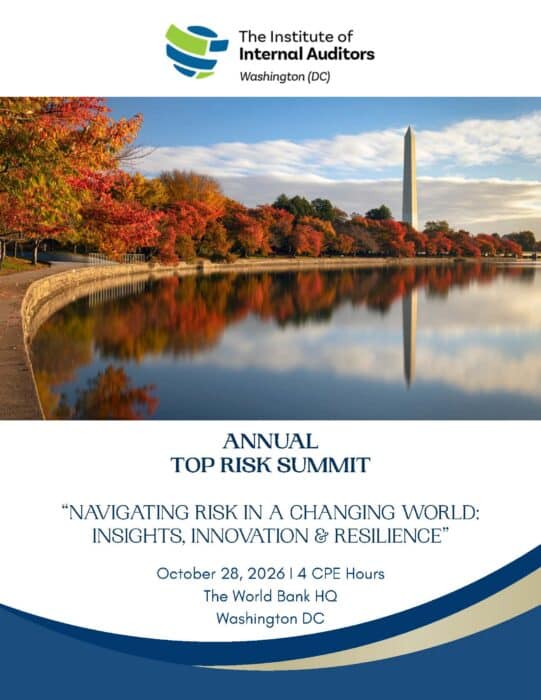
2026 IIA DC Annual Top Risks Summit
Navigating Risk In A Changing World: Insights, Innovation & Resilience
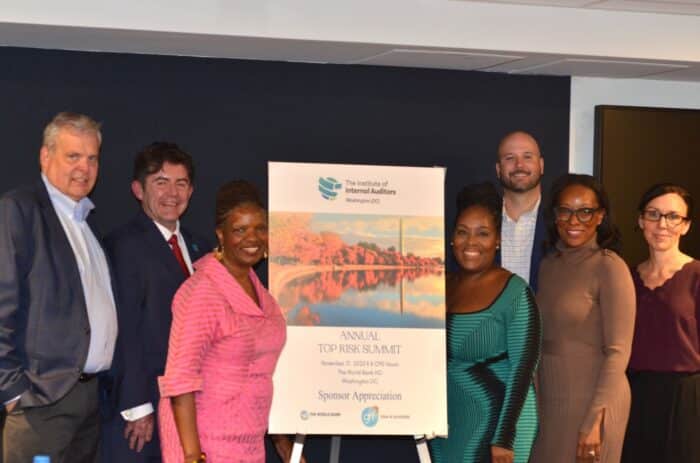 GRF is proud to be a founding sponsor of the IIA DC Annual Top Risks Summit, supporting the event since its inception during Melissa Musser’s tenure as president of the IIA Washington, DC Chapter. Now in its fourth year, the summit brings together leaders in internal audit, risk management, and governance.
Join GRF’s Risk & Advisory Services team as sponsors, presenters, and exhibitors on October 28 at World Bank headquarters—and earn 4 CPE credits for just $55 for nonmembers or $30 for IIA members.
Who Should Attend
- Senior-Level Managers and Executives
- Enterprise Risk Leaders
- Audittors
- Accountants
- CIAs, CPAs, CGFMs, ACCAs, CISAs
Pricing
- IIA Members:$30
- Non-IIA Members: $55
- Students: Free
Learning Objectives
At the end of the Risk Summit, participants will be able to identify key trends and challenges shaping the Internal Audit profession; explain approaches for strengthening risk management, internal controls, governance, and oversight; recognize emerging cybersecurity risks and related audit priorities; and describe how organizations can build trust, readiness, and resilience in an AI-enabled workforce.
Discussion Topics
-
- The State of the IA Profession
- Risk Management and Internal Controls in a Changing Risk Environment: Governance, Implementation, and Oversight
- Cybersecurity Risks and Audit Priorities for 2026-2027
- The Human Side of AI: Building Trust, Readiness, and Resilience in an AI-Enabled Workforce
Meet the team!
GRF’s Melissa Musser, Darren Hulem, and Tom Brown (IIA DC Chapter’s Assistant VP Programs) will be on hand. Stop by our exhibit table to learn more about our internal audit, ERM, and cybersecurity services.
Featured Presentation
Cybersecurity and Audit Priorities for 2026-2027 | October 28, 2026, 12:30 pm – 1:30 pm
Speakers:
- Melissa Musser, CPA, CIA, CITP, CISA | Partner and Director, Risk & Advisory Services | GRF CPAs & Advisors
- Darren Hulem, CISA, CEH, Security +, CMMC Lead CCA/CCP | Senior Manager, Risk & Advisory Services | GRF CPAs & Advisors
As cyber threats, technologies, and regulatory expectations evolve, organizations must reassess whether their cybersecurity controls and audit plans address the most significant areas of risk. In this presentation, GRF’s Melissa Musser and Darren Hulem will examine the cybersecurity risks expected to shape 2026–2027, the controls organizations should prioritize, and how internal audit and leadership can provide meaningful oversight of cybersecurity preparedness and resilience.